01
Featured lab · Windows infrastructure
Enterprise Active Directory Deployment
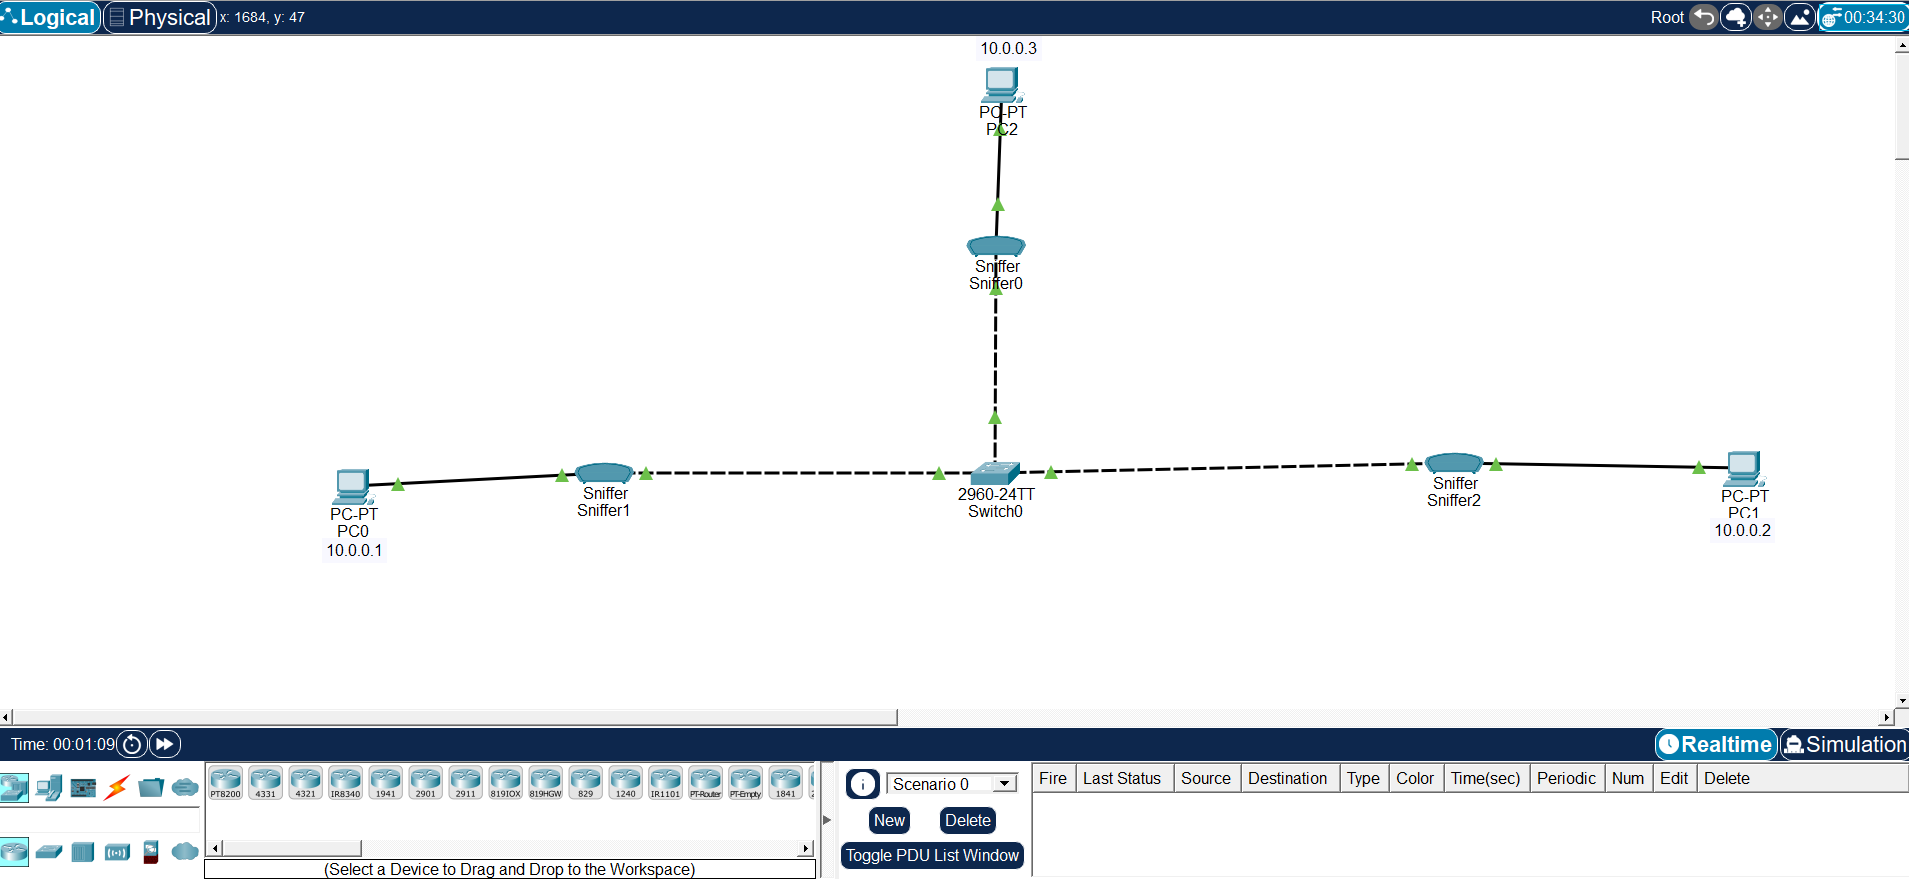
Built a simulated Windows Server environment for a small business that needed centralized sign-in, consistent network configuration, and secure departmental file access.
- BuiltDeployed the kalomba.local domain with AD DS, DNS, DHCP, and IT, HR, and Sales user groups.
- SecuredApplied password and desktop policies through GPO; restricted department shares with NTFS and share permissions.
- ValidatedJoined client PCs to the domain, checked sign-in, DHCP and DNS, verified policies, and tested allowed versus denied file access.